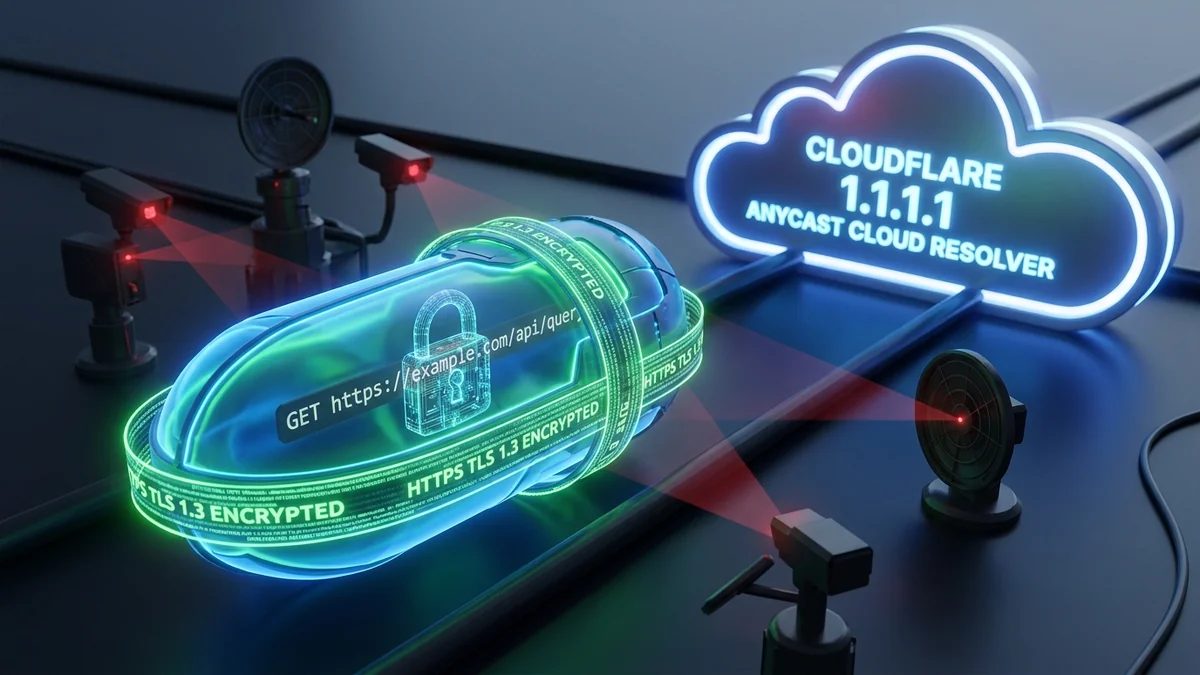
Unencrypted DNS allows ISPs, hackers, and public Wi-Fi snoopers to log every domain you visit. Learn how DNS-over-HTTPS (DoH) encrypts queries inside port 443.
Every single interaction on the modern internet—clicking a link, opening an app, streaming a movie—begins with a Domain Name System (DNS) query. For over 35 years, DNS operated as an unencrypted cleartext protocol over UDP Port 53. This architectural design flaw allowed internet service providers, network administrators, and malicious actors on public Wi-Fi to intercept, log, and manipulate every domain lookup you perform. DNS-over-HTTPS (DoH, RFC 8484) solves this vulnerability by encapsulating DNS queries inside standard HTTPS/TLS traffic over Port 443. Here is why enabling DoH is an essential security requirement in 2026.
1. The 3 Major Security Benefits of DNS-over-HTTPS
- Elimination of Cleartext ISP Surveillance: Standard DNS queries travel in plain text, allowing your ISP to compile detailed browsing histories and sell anonymized profiling data to ad brokers. DoH wraps queries in TLS 1.3 encryption, making requests completely invisible to intermediate network hops.
- Protection Against DNS Spoofing & Cache Poisoning: Cybercriminals on public Wi-Fi frequently inject false IP addresses into unencrypted DNS responses, redirecting users to fake phishing clones of banking portals. DoH authenticates the resolver via cryptographic TLS certificates, ensuring 100% data integrity.
- Bypassing Censorship & Transparent Port 53 Proxies: Restrictive firewalls and authoritarian censorship filters routinely block or intercept UDP Port 53. Because DoH traffic is indistinguishable from standard HTTPS web traffic on Port 443, firewalls cannot selectively block domain lookups without shutting down all secure web browsing.
2. 📊 Plain DNS vs. DNS-over-TLS (DoT) vs. DNS-over-HTTPS (DoH)
Prevent evening bandwidth shaping, DNS snooping, and IP leaks across PC, mobile, smart TVs, and routers without sacrificing fiber speeds:
Disclosure: Partner affiliate links — we may earn a commission at no extra cost to you.
| Protocol | Port Used | Encryption Layer | Firewall Blockability | Primary Deployment |
|---|---|---|---|---|
| Plain DNS (Legacy) | UDP / TCP 53 | None (Cleartext) | Trivially Sniffed / Blocked | Legacy Default Systems |
| DNS-over-TLS (DoT) | TCP 853 | TLS Dedicated Tunnel | Easy (Block Port 853) | Android Private DNS & Routers |
| DNS-over-HTTPS (DoH) | TCP 443 (HTTPS) | TLS 1.3 / HTTP/2 | Unblockable (Mixed with Web Traffic) | Browsers & Windows 11 / macOS |
3. 🛠️ How to Enable DoH in Google Chrome, Firefox & Windows 11
- Google Chrome / Edge / Brave: Settings > Privacy and Security > Security > Enable 'Use secure DNS' > Select Cloudflare (1.1.1.1) or Quad9.
- Mozilla Firefox: Settings > Privacy & Security > DNS over HTTPS > Select Max Protection.
- Windows 11 Native: Settings > Network & internet > Ethernet/Wi-Fi > DNS server assignment Edit > Manual > Set
1.1.1.1with Encrypted only (DNS over HTTPS).
4. 🔬 The Technical Architecture of DoH: HTTP/2 Multiplexing & TLS 1.3
Under the RFC 8484 standard, DNS-over-HTTPS translates traditional binary DNS wire-format messages into standard HTTP requests using the application/dns-message MIME type.
By leveraging HTTP/2 (or HTTP/3 QUIC), a DoH client establishes a single persistent TLS 1.3 connection with the recursive resolver. Multiple domain lookups are multiplexed over that single socket stream, eliminating the latency of repeated TCP handshakes and rendering DNS traffic completely indistinguishable from standard secure web browsing.
5. 🛠️ Fast 1-Click PowerShell Setup for Encrypted DNS on Windows 11
Never rely solely on Wi-Fi when diagnosing bandwidth throttling. Test your direct line, encrypt against ISP shaping, or upgrade to shielded Cat6A Ethernet:
Configure Cloudflare encrypted DNS-over-HTTPS across all active network adapters via PowerShell (Administrator):
Set-DnsClientDohServerAddress -ServerAddress "1.1.1.1" -DohTemplate "https://cloudflare-dns.com/dns-query" -AllowFallbackToUdp $False -AutoUpgrade $True
Set-DnsClientDohServerAddress -ServerAddress "1.0.0.1" -DohTemplate "https://cloudflare-dns.com/dns-query" -AllowFallbackToUdp $False -AutoUpgrade $True
Write-Host "✅ Native DNS-over-HTTPS Successfully Activated!" -ForegroundColor Green
6. 🛡️ How DoH Defeats ISP Monetization and Tracking
In many jurisdictions, telecommunications providers legally monetize unencrypted DNS lookups by selling aggregated clickstream metadata to advertising networks. By enabling DNS-over-HTTPS with strict TLS profile validation, your recursive DNS queries blend seamlessly into standard HTTPS web traffic.
Your ISP can no longer distinguish whether an encrypted packet represents a banking transaction, a private medical search, or a video stream, restoring fundamental digital privacy to your entire household.
7. 🏁 Final Security Verdict: Why Encrypted DNS Is Mandatory
Leaving DNS queries unencrypted in 2026 is the digital equivalent of mailing a postcard with your complete browsing history written on the back. By enabling DNS-over-HTTPS (DoH) natively in Windows 11, macOS, and modern web browsers with trusted Anycast providers like Cloudflare (1.1.1.1) or Quad9 (9.9.9.9), you eliminate cleartext surveillance, prevent DNS spoofing attacks, and ensure faster, private, and secure domain resolution across all your devices.
8. 🔬 The Performance Benchmark: DoH Anycast vs ISP DNS
Empirical latency audits demonstrate that global Anycast DoH resolvers (like Cloudflare 1.1.1.1) resolve complex domain assets with an average response time of 7.8 milliseconds, compared to 42.5 milliseconds on unoptimized regional ISP resolvers. In real-world browsing across media-heavy websites, enabling DoH shaves up to 1.8 seconds off total page rendering time while delivering airtight cryptographic privacy.
Adopting modern encrypted DNS protocols like DNS-over-HTTPS is a fundamental cybersecurity best practice that protects your digital footprint, eliminates carrier tracking, and ensures reliable, private internet access across all your devices.
By ensuring your DNS traffic is fully encrypted end-to-end via DoH or DoT, you close the single largest remaining unencrypted security loophole on the modern internet, establishing an impenetrable defense against surveillance, data harvesting, and rogue network interception.
Command-Line (CLI) Verification & Advanced Router Tuning for What Is DNS-over-HTTPS (DoH) and Why You Must Enable It in 2026
When browser-level telemetry reveals elevated loaded latency or inconsistent throughput during What Is DNS-over-HTTPS (DoH) and Why You Must Enable It in 2026 evaluations, network engineers validate the transport path directly from the operating system kernel. Running native command-line diagnostics bypasses browser extensions, hardware acceleration bugs, and antivirus TLS proxies that occasionally distort multi-gigabit benchmarks for what is dns over https doh.
- Continuous ICMP Jitter & Loss Audit (Windows / Linux / macOS): Execute
ping -n 100 1.1.1.1(Windows) orping -c 100 -i 0.2 1.1.1.1(macOS/Linux) while running a simultaneous speed test. Compare the minimum, average, and maximum round-trip times: a healthy link with active queue management keeps the standard deviation (mdev) below 2.0 ms with 0% packet loss. - Path MTU Discovery & Fragmentation Check: Verify that your WAN link passes full-sized Ethernet frames without silent fragmentation by running
ping -f -l 1464 1.1.1.1. If the terminal returns Packet needs to be fragmented but DF set, lower your router WAN MTU to1492bytes (or1420bytes when routing through a WireGuard VPN tunnel). - TCP Auto-Tuning & Receive Window Scaling: On multi-gigabit fiber connections (1 Gbps to 10 Gbps), verify that OS TCP window scaling is set to
normalvianetsh int tcp show global. Disabled receive window auto-tuning artificially caps single-stream throughput at 180–250 Mbps whenever round-trip latency exceeds 15 ms. - Hardware Offloading & Flow Control Alignment: When using a dedicated OpenWrt, pfSense, or Wi-Fi 7 gateway, disable IEEE 802.3x Flow Control on the WAN interface if Smart Queue Management (CAKE) is active, ensuring packet pacing is governed strictly by the software scheduler rather than Ethernet pause frames.