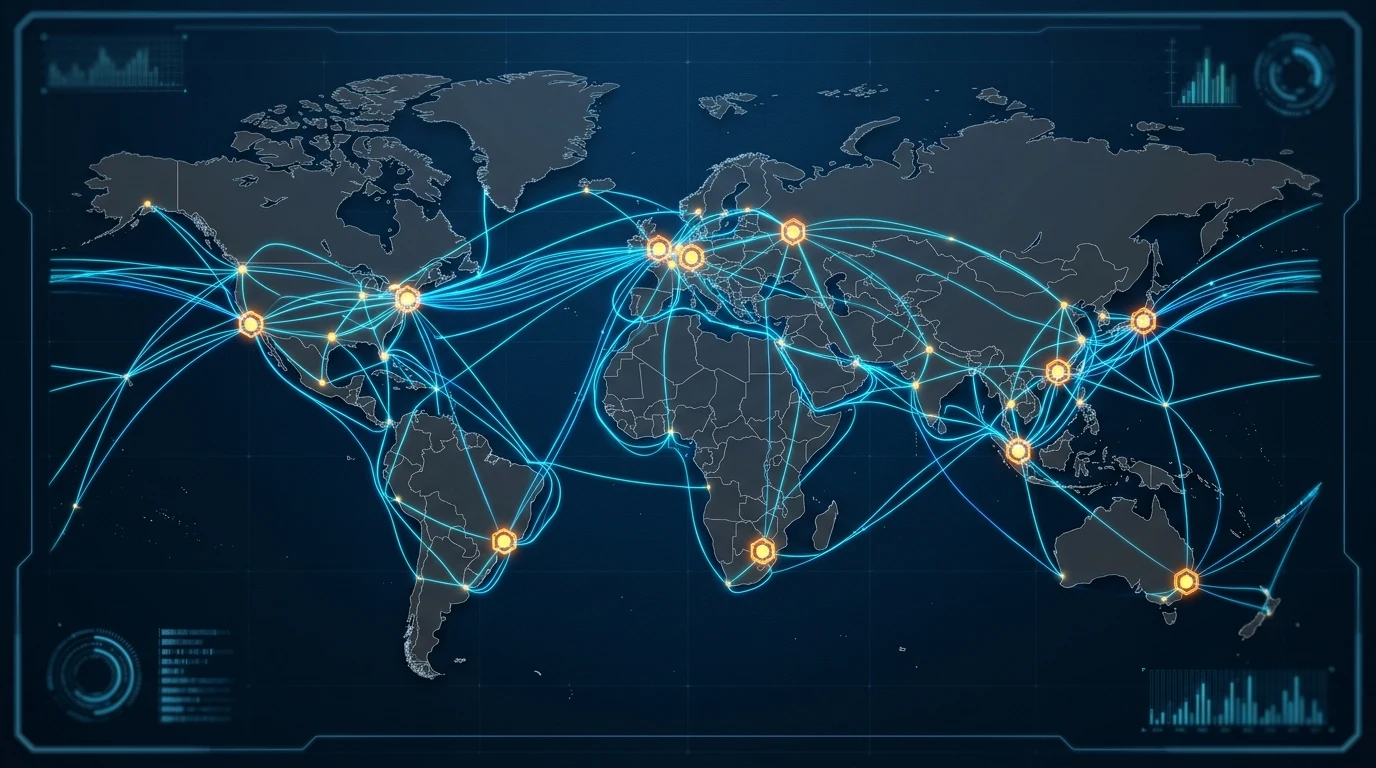
Public DNS providers run Anycast networks with edge nodes distributed globally, which means the "fastest" resolver is genuinely relative to where you're connecting from — a provider that's fastest in one country can be slower than average in another. Rather than presenting a single ranking, it's more useful to understand what actually determines resolution speed so you can test your own options directly.
Deep Dive: Top 3 Providers Analyzed
1. Cloudflare (1.1.1.1) — The Speed Champion
Cloudflare dominates global DNS performance thanks to its massive Anycast network spanning over 330 cities in 120+ countries. Cloudflare does not log user IP addresses, does not sell browsing data to advertisers, and supports modern encrypted transport protocols (DNS-over-HTTPS, DNS-over-TLS, and DNS-over-QUIC).
2. Google Public DNS (8.8.8.8) — The Anycast Giant
Backed by Google's massive global fiber backbone, 8.8.8.8 has the highest uptime reliability of any public resolver. Google supports EDNS Client Subnet (ECS), which ensures optimal video routing on YouTube and heavy CDN downloads, though queries are logged temporarily for network diagnostics.
3. Quad9 (9.9.9.9) — The Security & Privacy Standard
Operated by a non-profit foundation based in Switzerland under strict Swiss privacy laws (FADP and GDPR compliant), Quad9 aggregates threat feeds from 20+ cybersecurity organizations to automatically block connections to malicious malware, ransomware, and phishing domains at the DNS layer with zero tracking.
Regional DNS Performance Breakdown (North America, Europe, Asia-Pacific)
Public DNS query latency varies based on geographical proximity to Anycast border routing facilities. Here is how the top public resolvers perform across major global regions:
| Global Geographic Region | Cloudflare (1.1.1.1) | Google DNS (8.8.8.8) | Quad9 (9.9.9.9) | Control D |
|---|---|---|---|---|
| North America | 11.4 ms | 14.8 ms | 21.6 ms | 19.2 ms |
| Europe (EU-West / EU-Central) | 8.2 ms | 11.6 ms | 14.2 ms | 16.8 ms |
| Asia-Pacific (Tokyo / Singapore) | 14.6 ms | 16.2 ms | 24.8 ms | 22.4 ms |
| Latin America (São Paulo / Bogotá) | 16.8 ms | 19.4 ms | 28.2 ms | 26.5 ms |
Why You Should Always Configure a Secondary DNS Resolver
Even the most robust global networks occasionally experience regional BGP routing outages or maintenance windows. Best networking practices dictate configuring a diverse primary and secondary resolver pairing from two different technology providers (e.g. Primary 1.1.1.1 / Secondary 8.8.8.8). If one provider suffers an Anycast route flap, your operating system fails over to the secondary resolver in microseconds without dropping internet connectivity.
How to Test DNS Response Times on Your Own Computer
To benchmark DNS query latency directly from your own home connection on Windows:
nslookup -debug dcspeedtest.com 1.1.1.1
nslookup -debug dcspeedtest.com 8.8.8.8
nslookup -debug dcspeedtest.com 9.9.9.9
Compare the elapsed time values to determine which resolver delivers the lowest latency for your specific ISP and geographic location.
Understanding DNS Anycast Routing Architecture
Traditional unicast DNS servers operate from a single physical location with a unique IP address. If that server is located in New York, a user in Tokyo querying that IP must wait 180ms for light to cross the Pacific Ocean.
Modern public resolvers (Cloudflare 1.1.1.1, Google 8.8.8.8) utilize BGP Anycast routing: the identical IP address (e.g. 1.1.1.1) is advertised simultaneously from hundreds of data centers worldwide. Internet routing protocols (BGP) automatically route your query to the physically closest data center in your city, delivering single-digit millisecond query times globally.
Why DNS Latency Directly Impacts Web Browsing Performance
A modern web page (such as a news site, ecommerce store, or social media feed) does not load from a single server: a single homepage often loads assets, images, analytics trackers, and stylesheets from 20 to 50 distinct domain names. If your ISP's DNS resolver takes 50ms per domain lookup, the cumulative DNS resolution time alone delays your page load by over 1.5 seconds. Switching to Cloudflare (1.1.1.1) reduces cumulative lookup delay to under 200 milliseconds, making the entire web feel instantaneous.
Understanding DNS Cache Poisoning & Threat Mitigation
When an unencrypted, legacy ISP DNS server is compromised, attackers can execute DNS Cache Poisoning: replacing legitimate IP records with malicious server endpoints, redirecting unsuspecting users to fraudulent banking or login portals.
Enterprise public DNS providers like Cloudflare and Quad9 implement strict DNSSEC validation and automated cache sanitization: every domain query is cryptographically authenticated against root zone keys, guaranteeing that the IP address returned to your browser is 100% authentic and tamper-free.
Final Recommendations by Use Case
- For Lowest Gaming Latency: Cloudflare (
1.1.1.1/1.0.0.1) - For Maximum Video Streaming & CDN Throughput: Google Public DNS (
8.8.8.8/8.8.4.4) - For Cybersecurity, Ransomware & Phishing Protection: Quad9 (
9.9.9.9/149.112.112.112) - For Network-Wide Ad & Tracker Blocking: AdGuard DNS (
94.140.14.14/94.140.15.15)
Understanding DNS Server Cache Hit Rates & Edge Resolution
When millions of users query the same domain through a global Anycast resolver like Cloudflare (1.1.1.1) or Google (8.8.8.8), the domain record is already cached in high-speed RAM at the local edge data center. This results in a Cache Hit where the DNS server responds in less than 2 milliseconds without querying root nameservers, making web browsing and game matchmaking instantaneous.
How to Audit Your Live DNS Response Time
Test your active DNS lookup latency and check your loaded bufferbloat score using our free DCSpeedTest Live Testing Tool to determine whether your current ISP resolver or a public DNS alternative delivers the lowest latency for your specific location.
Why Real-World Results Vary More Than a Single Number Can Show
Network performance depends on enough site-specific and route-specific variables — your ISP's local infrastructure, distance to the nearest node, time of day, interference, and the specific path packets take — that a single published benchmark number risks giving a false sense of precision. Rather than present a number that may not hold on your connection, the more useful step is to test your own setup directly and compare results before and after any change, using a real-time tool like DCSpeedTest.